
Go to the “⚙” – “For developers” page in HURMA.
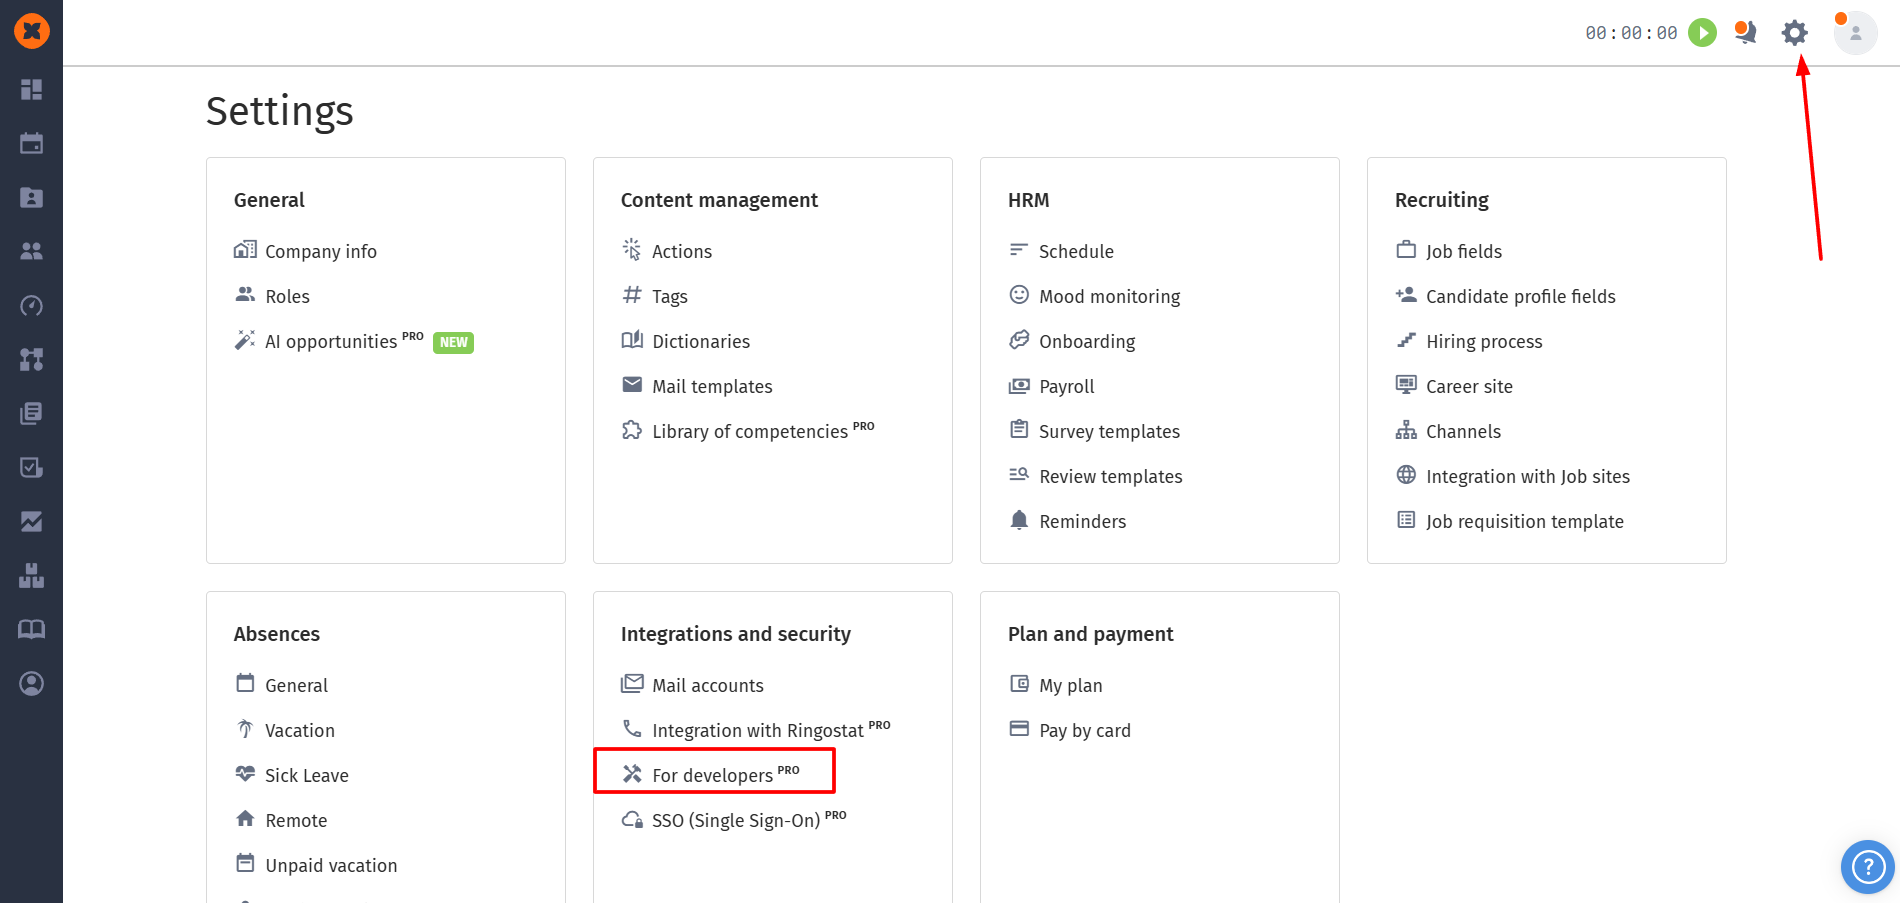
Click the “Add API Client” button. In the form that opens, fill in the following fields:
Title – any name for your application (e.g., "ERP Integration").
Authorization Type
Authorization code – recommended for external applications with user authorization (via OAuth 2.0).
Password – direct exchange of login and password for a token (used in trusted integrations, e.g., backend-to-backend).
Redirect – the address where the system will send the authorization code after the user logs in. This is a required field when using the “Authorization code” type.
Description – additional information or purpose of the integration (optional).
API Access Settings and Sensitive API Fields – a set of permissions that will be available to this application.
Click “Save” – after that, the application will appear in the list of generated clients. You will then receive the following data:
Client ID
Client Secret
These values will be required for authorization.
Integration with the HURMA API is possible using two methods:
This method is suitable if the integration involves user authorization through a user interface.
Generate an authorization request:
GET https://yourcompany.hurma.work/api/v3/oauth/authorize
?response_type=code
&client_id=YOUR_CLIENT_ID
&redirect_uri=YOUR_REDIRECT_URI
user authorizes → HURMA will redirect to your redirect_uri with a code in the URL parameters (?code=XXXXXX).
Exchange the code for an access token.
POST https://yourcompany.hurma.work/api/v3/oauth/token
Content-Type: application/x-www-form-urlencoded

grant_type=authorization_code
&client_id=YOUR_CLIENT_ID
&client_secret=YOUR_CLIENT_SECRET
&code=CODE_FROM_STEP_2
&redirect_uri=YOUR_REDIRECT_URI
Receive the access token in the response.
This method is suitable for server-side scenarios without user interaction.
Send a request for a token:
POST https://yourcompany.hurma.work/api/v3/oauth/token
Content-Type: application/x-www-form-urlencoded

grant_type=password
&client_id=YOUR_CLIENT_ID
&client_secret=YOUR_CLIENT_SECRET
&username=USER_EMAIL
&password=USER_PASSWORDAdd the obtained access_token to every API request:
GET /api/v3/users
Host: yourcompany.hurma.work
Authorization: Bearer YOUR_ACCESS_TOKENUse HTTPS for all requests.
Store your Client Secret in a secure location.
Do not use Password Flow in a browser.
Regularly update your access token using the refresh_token if the "Authorization Code" authorization type is used.
If you have any questions, you can contact our team:
via the in-system chat
by email at [email protected]
on Telegram
